Part VIII: Security under changing conditions
Controls and evidence can lose validity when the sector, operating conditions, or system capabilities change.
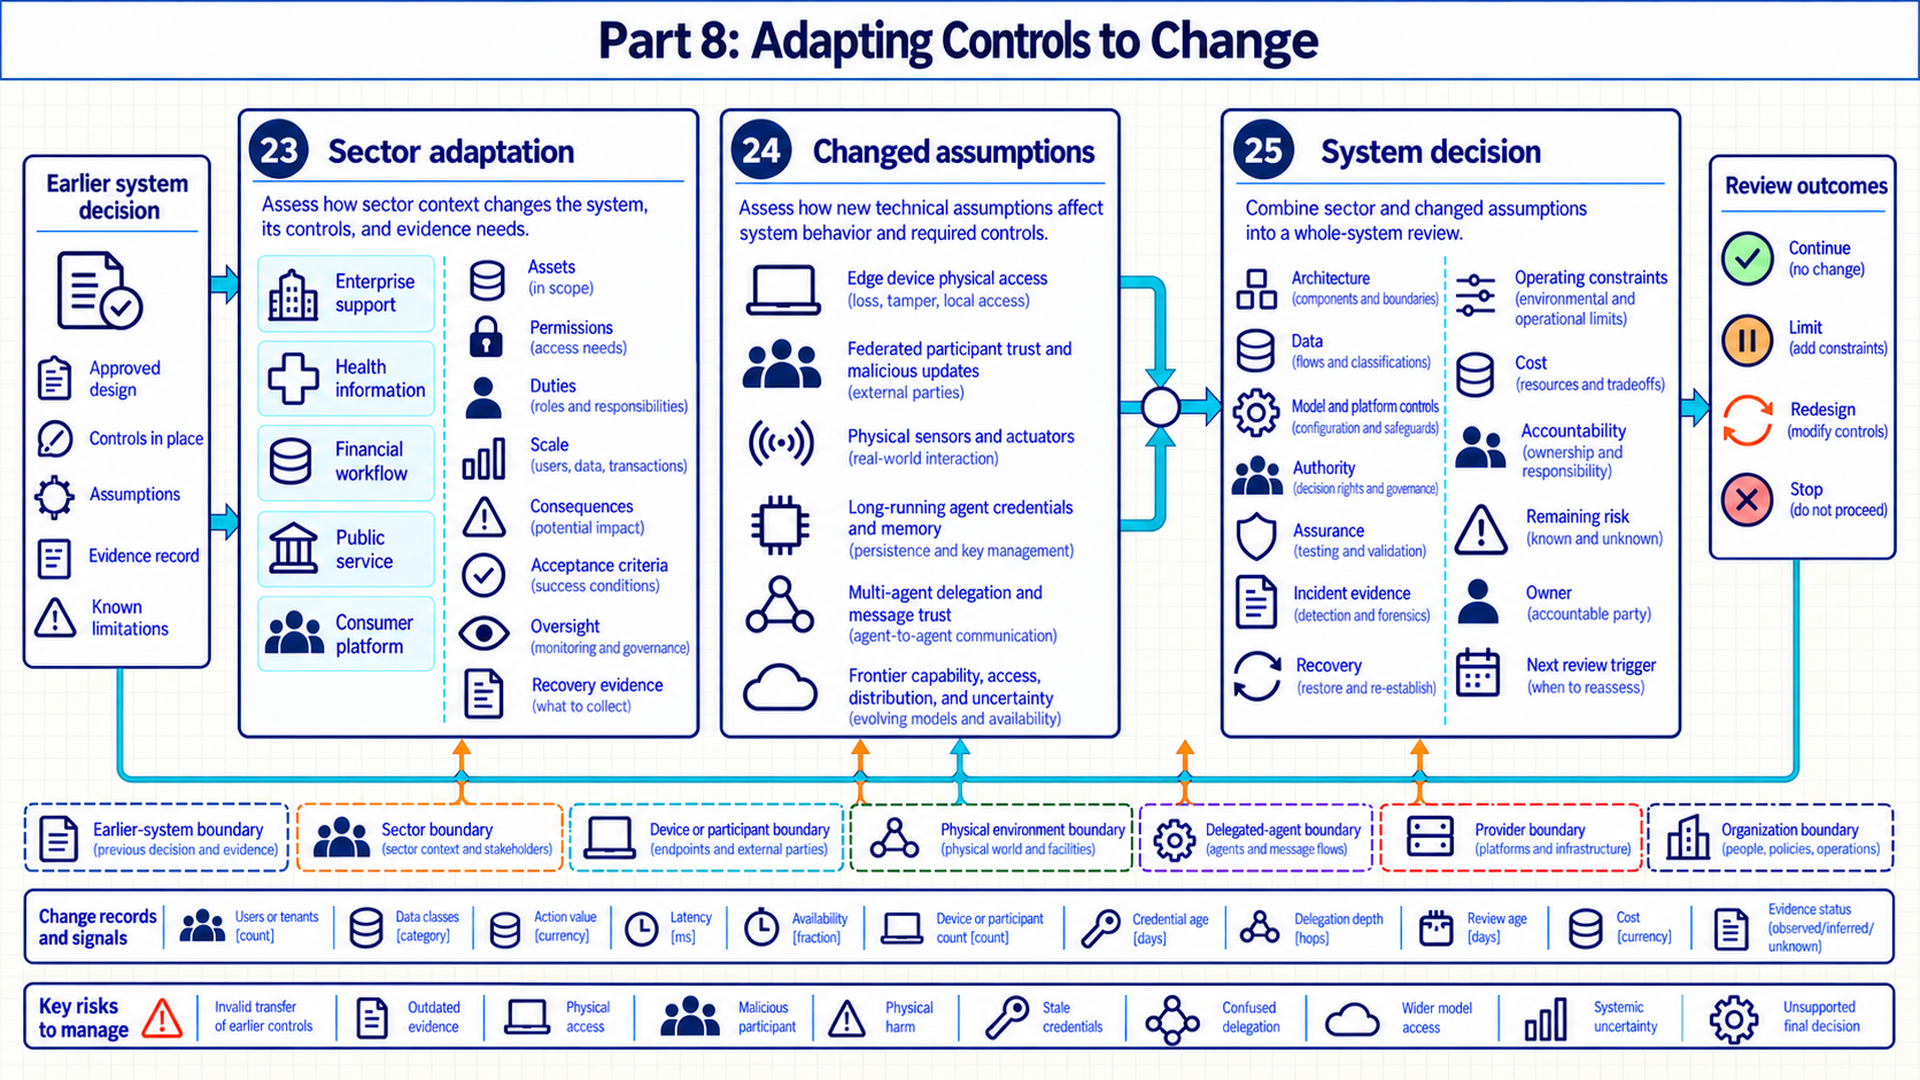
A control tested for one service may be inadequate when the data becomes more sensitive or an agent gains new permissions. Chapter 23 examines changes in sector duties, operating scale, and possible harm. Chapter 24 examines technical changes such as physical access, shared training, persistent memory, and delegation. The final case combines both kinds of change and asks which earlier evidence still supports a decision to continue, restrict, redesign, or stop the system.
Chapters in this part
- Adapting controls across sectors: A transfer review states which assets, duties, permissions, and consequences change before applying earlier controls to a new sector.
- Reassessing security after technology changes: Changes in physical access, participant trust, persistence, delegated authority, or systemic uncertainty reopen earlier security assumptions.
- Capstone: defending a system decision: A whole system review connects architecture, data, model and platform controls, authority, assurance, recovery, cost, and accountability in one decision.